
Probus
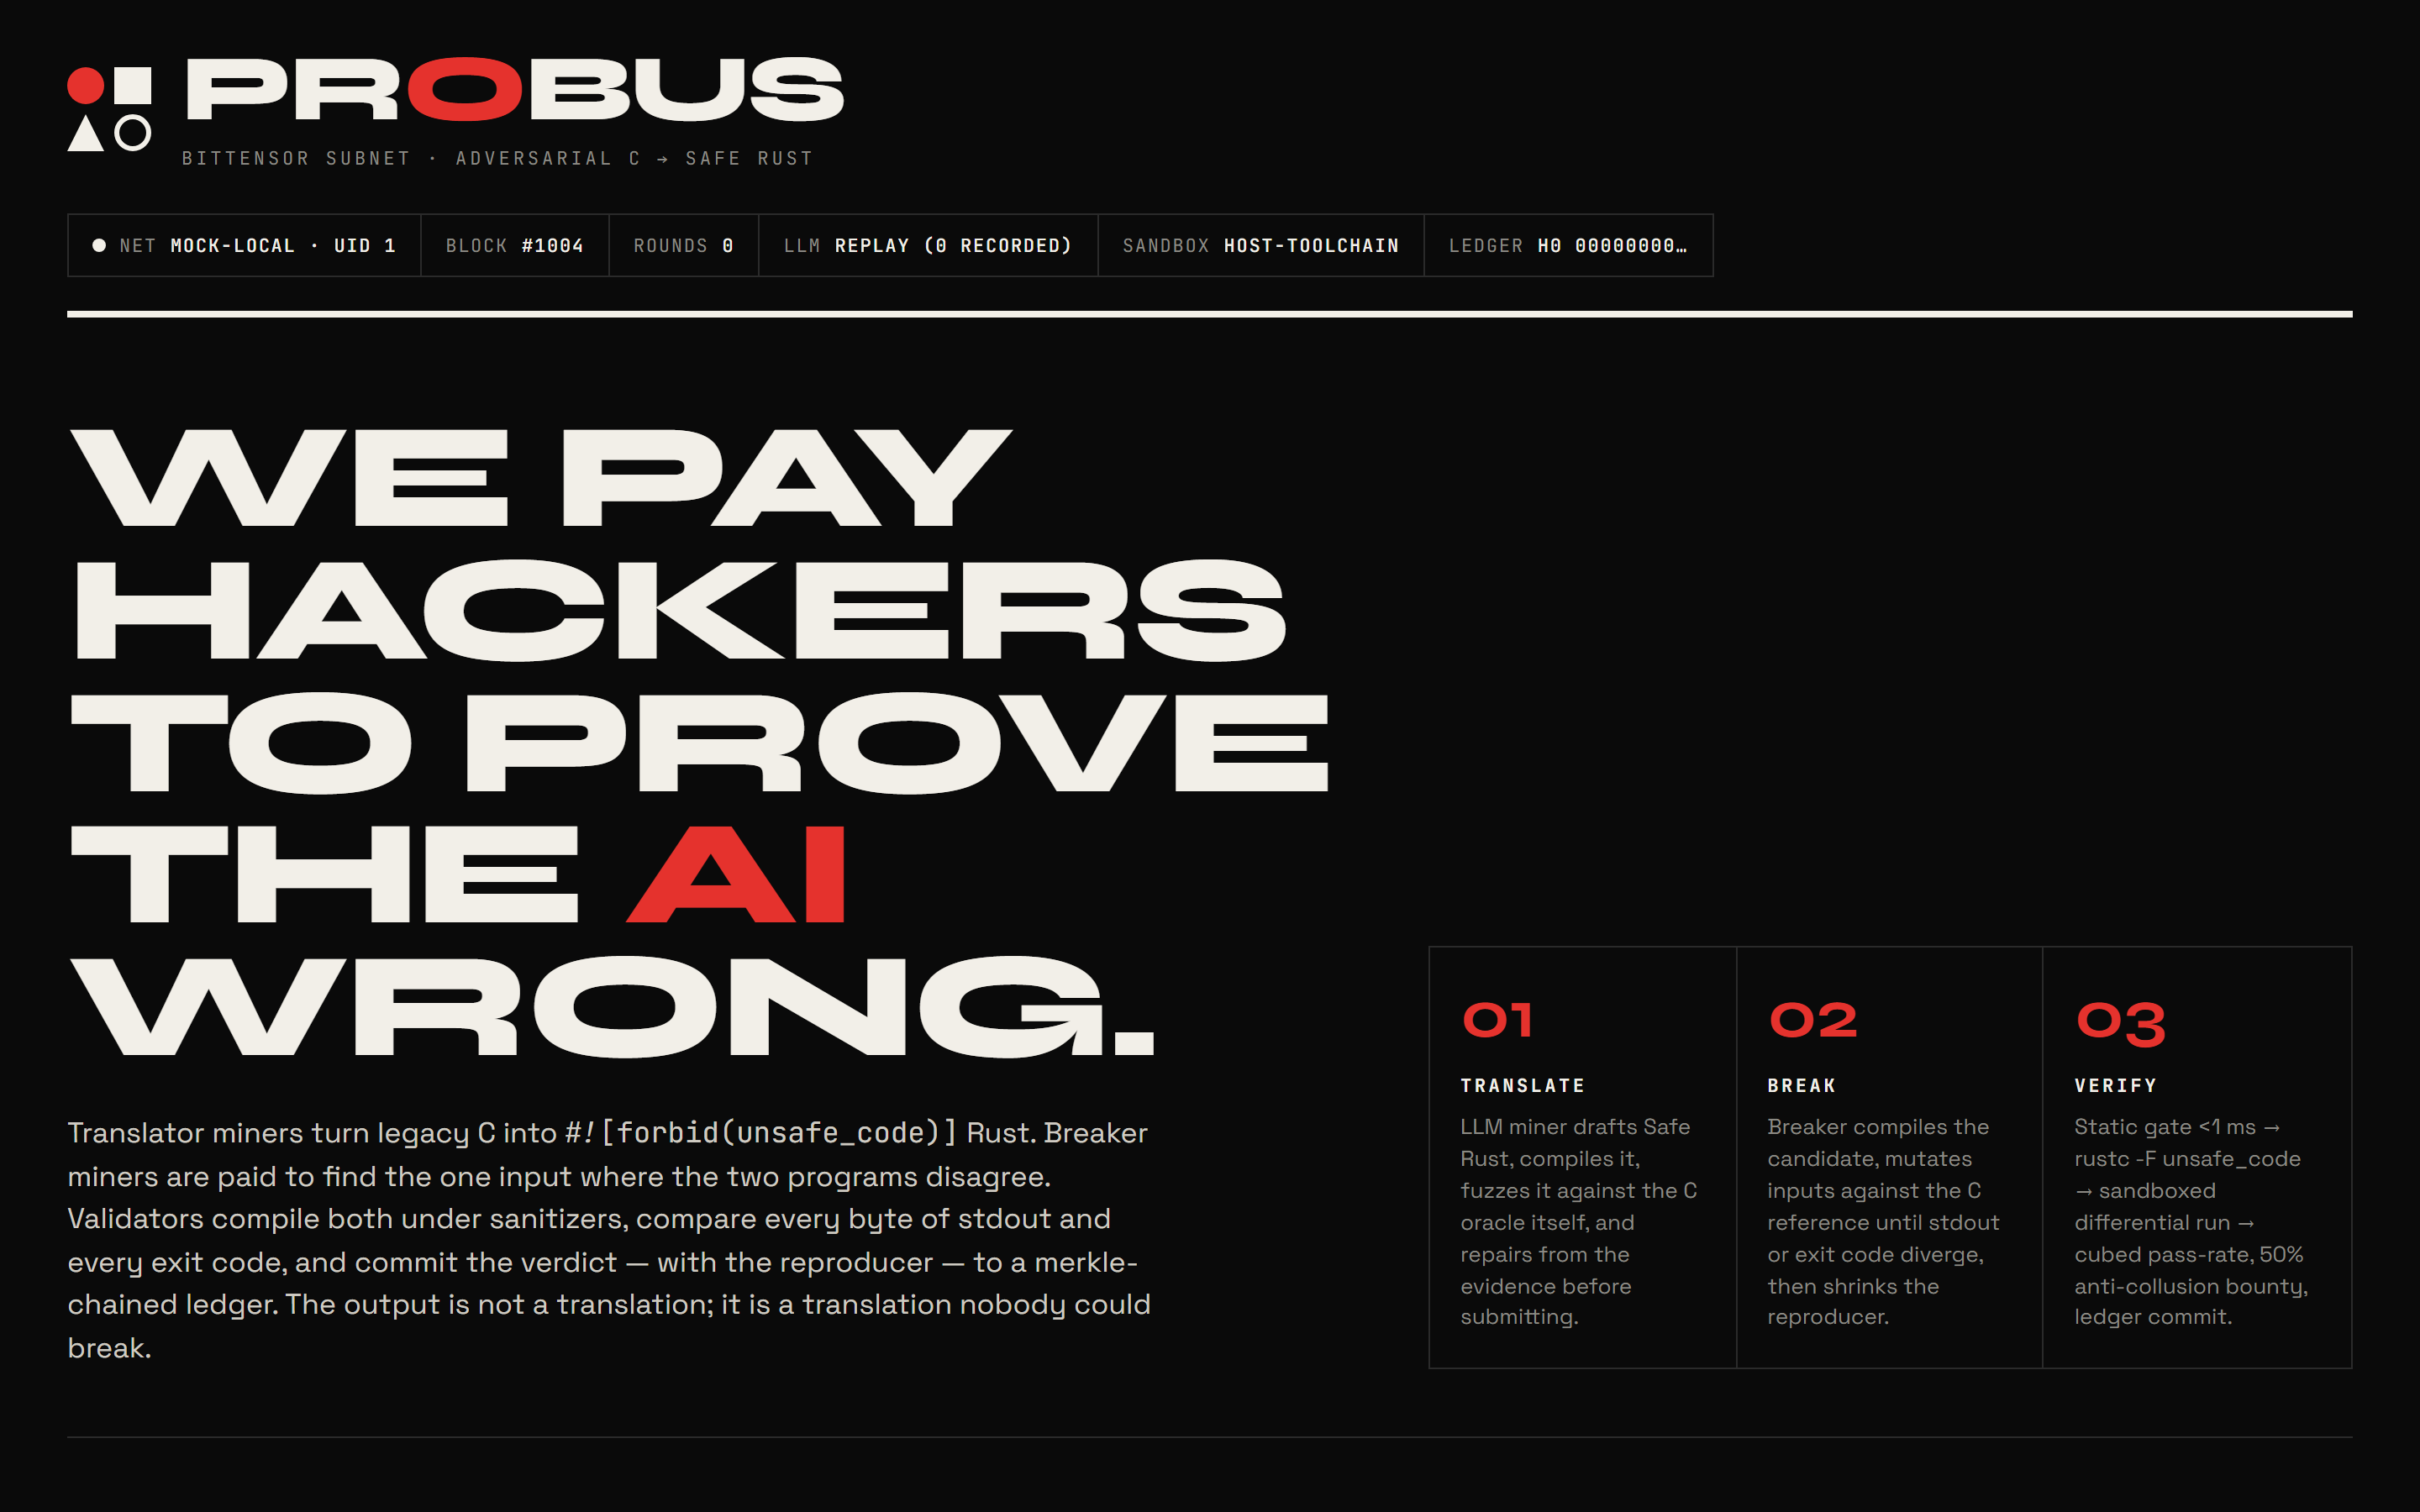
Probus turns C into memory-safe Rust, then pays hackers to break it—rewarding translations that survive adversarial fuzzing.
Videos
Tech Stack
Description
The problem. Legacy C runs critical infrastructure and leaks memory-safety CVEs every week. Governments and vendors are mandating migration to memory-safe languages, but automated C→Rust translators fail on exactly the inputs nobody tests — an overlong UTF-8 sequence, a line one byte longer than a buffer, an overflow bit in the last byte of a varint. A centralised "AI translation service" has no adversary. Nobody is paid to find its mistakes.
The subnet. Probus makes finding them the most profitable thing on the network.
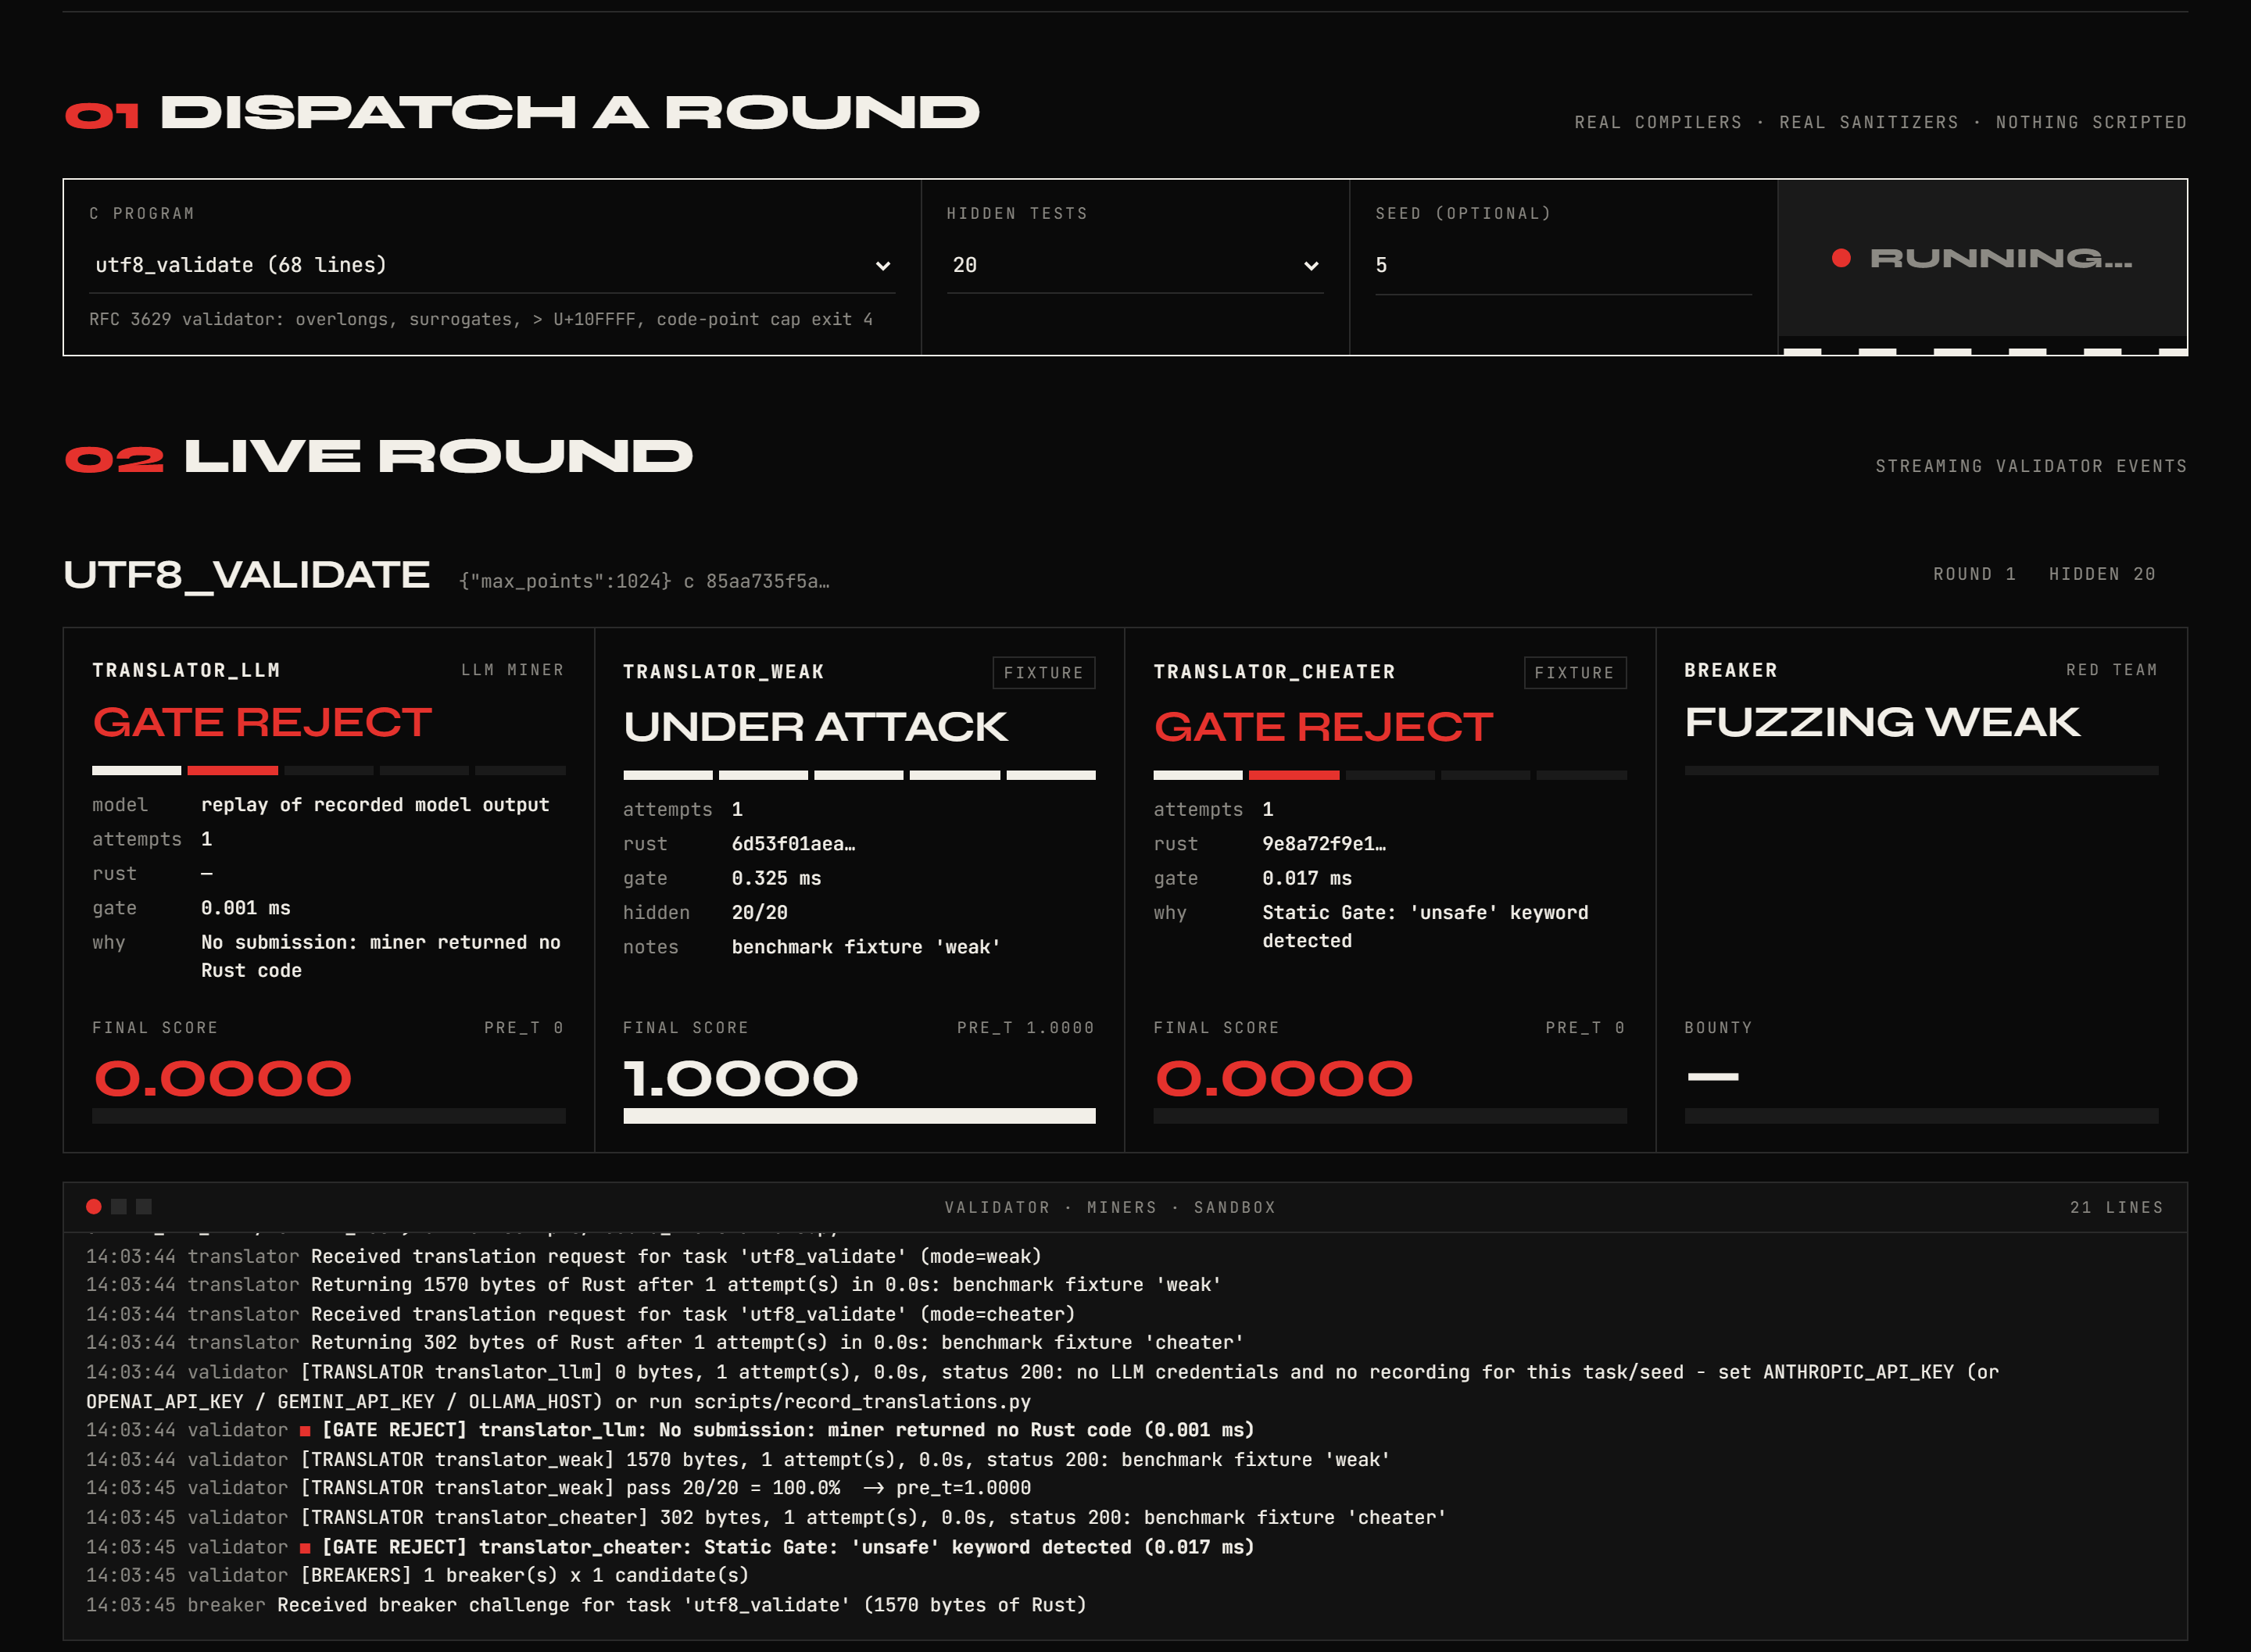
Translator miners receive a complete C program (stdin → stdout + exit code) and must return Safe Rust with identical observable behaviour. The miner prompts any LLM (Anthropic, OpenAI, Gemini, Ollama), then runs a local repair loop: static gate → rustc -F unsafe_code → differential fuzz against the C oracle → the failing input goes back to the model. It never sees a reference solution; a test greps the source to guarantee that.
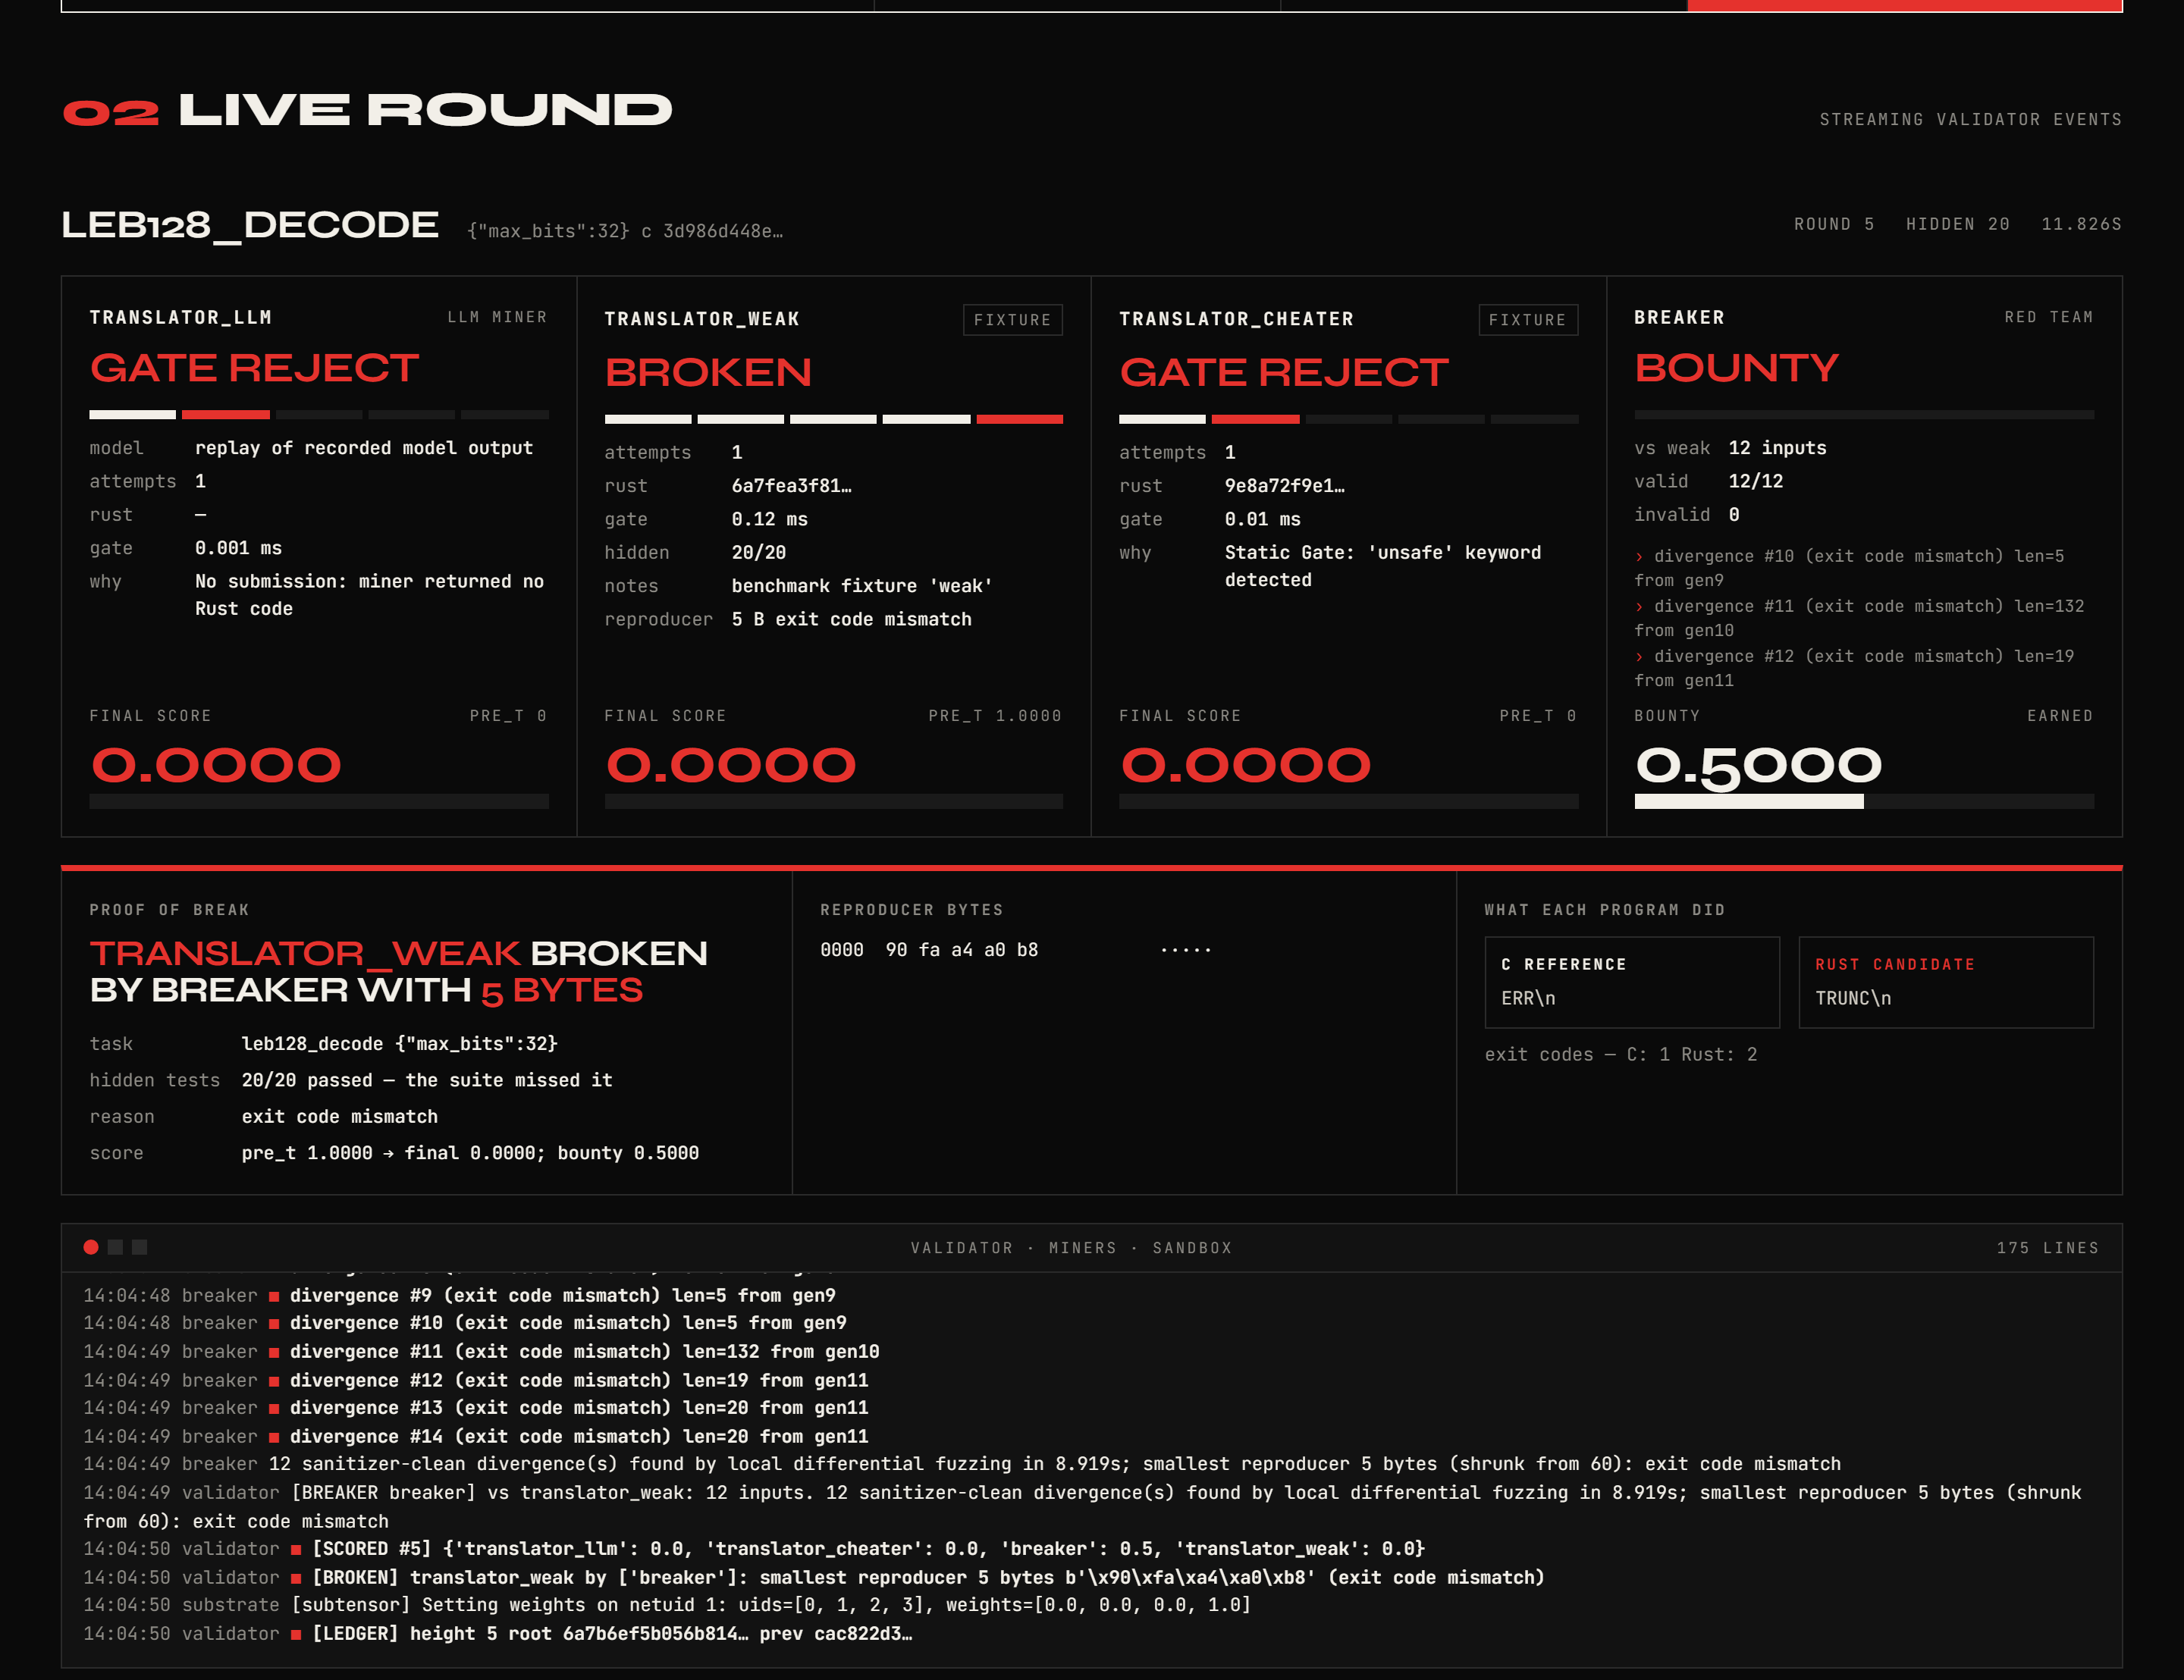
Breaker miners receive every compiling candidate. They read both sources for constants, mutate seed inputs against the C reference until stdout or exit code diverge, keep only inputs the ASan/UBSan build accepts (no UB farming), shrink each hit with delta debugging, and submit the smallest reproducer.
Validators compile in a throwaway container (--network none --read-only --cap-drop ALL), run a secret suite of structural boundary probes plus seeded fuzz, compare every byte of stdout and every exit code, then score:
translator
pre_t = (passed/total)³— 90% correct is worth 0.73, 50% is worth 0.125a broken translator scores 0 and its breakers split
0.5 · pre_t— planting a bug and "finding" it with a second hotkey nets −0.5·pre_tinvalid (UB-triggering) breaker inputs cost 0.05 each
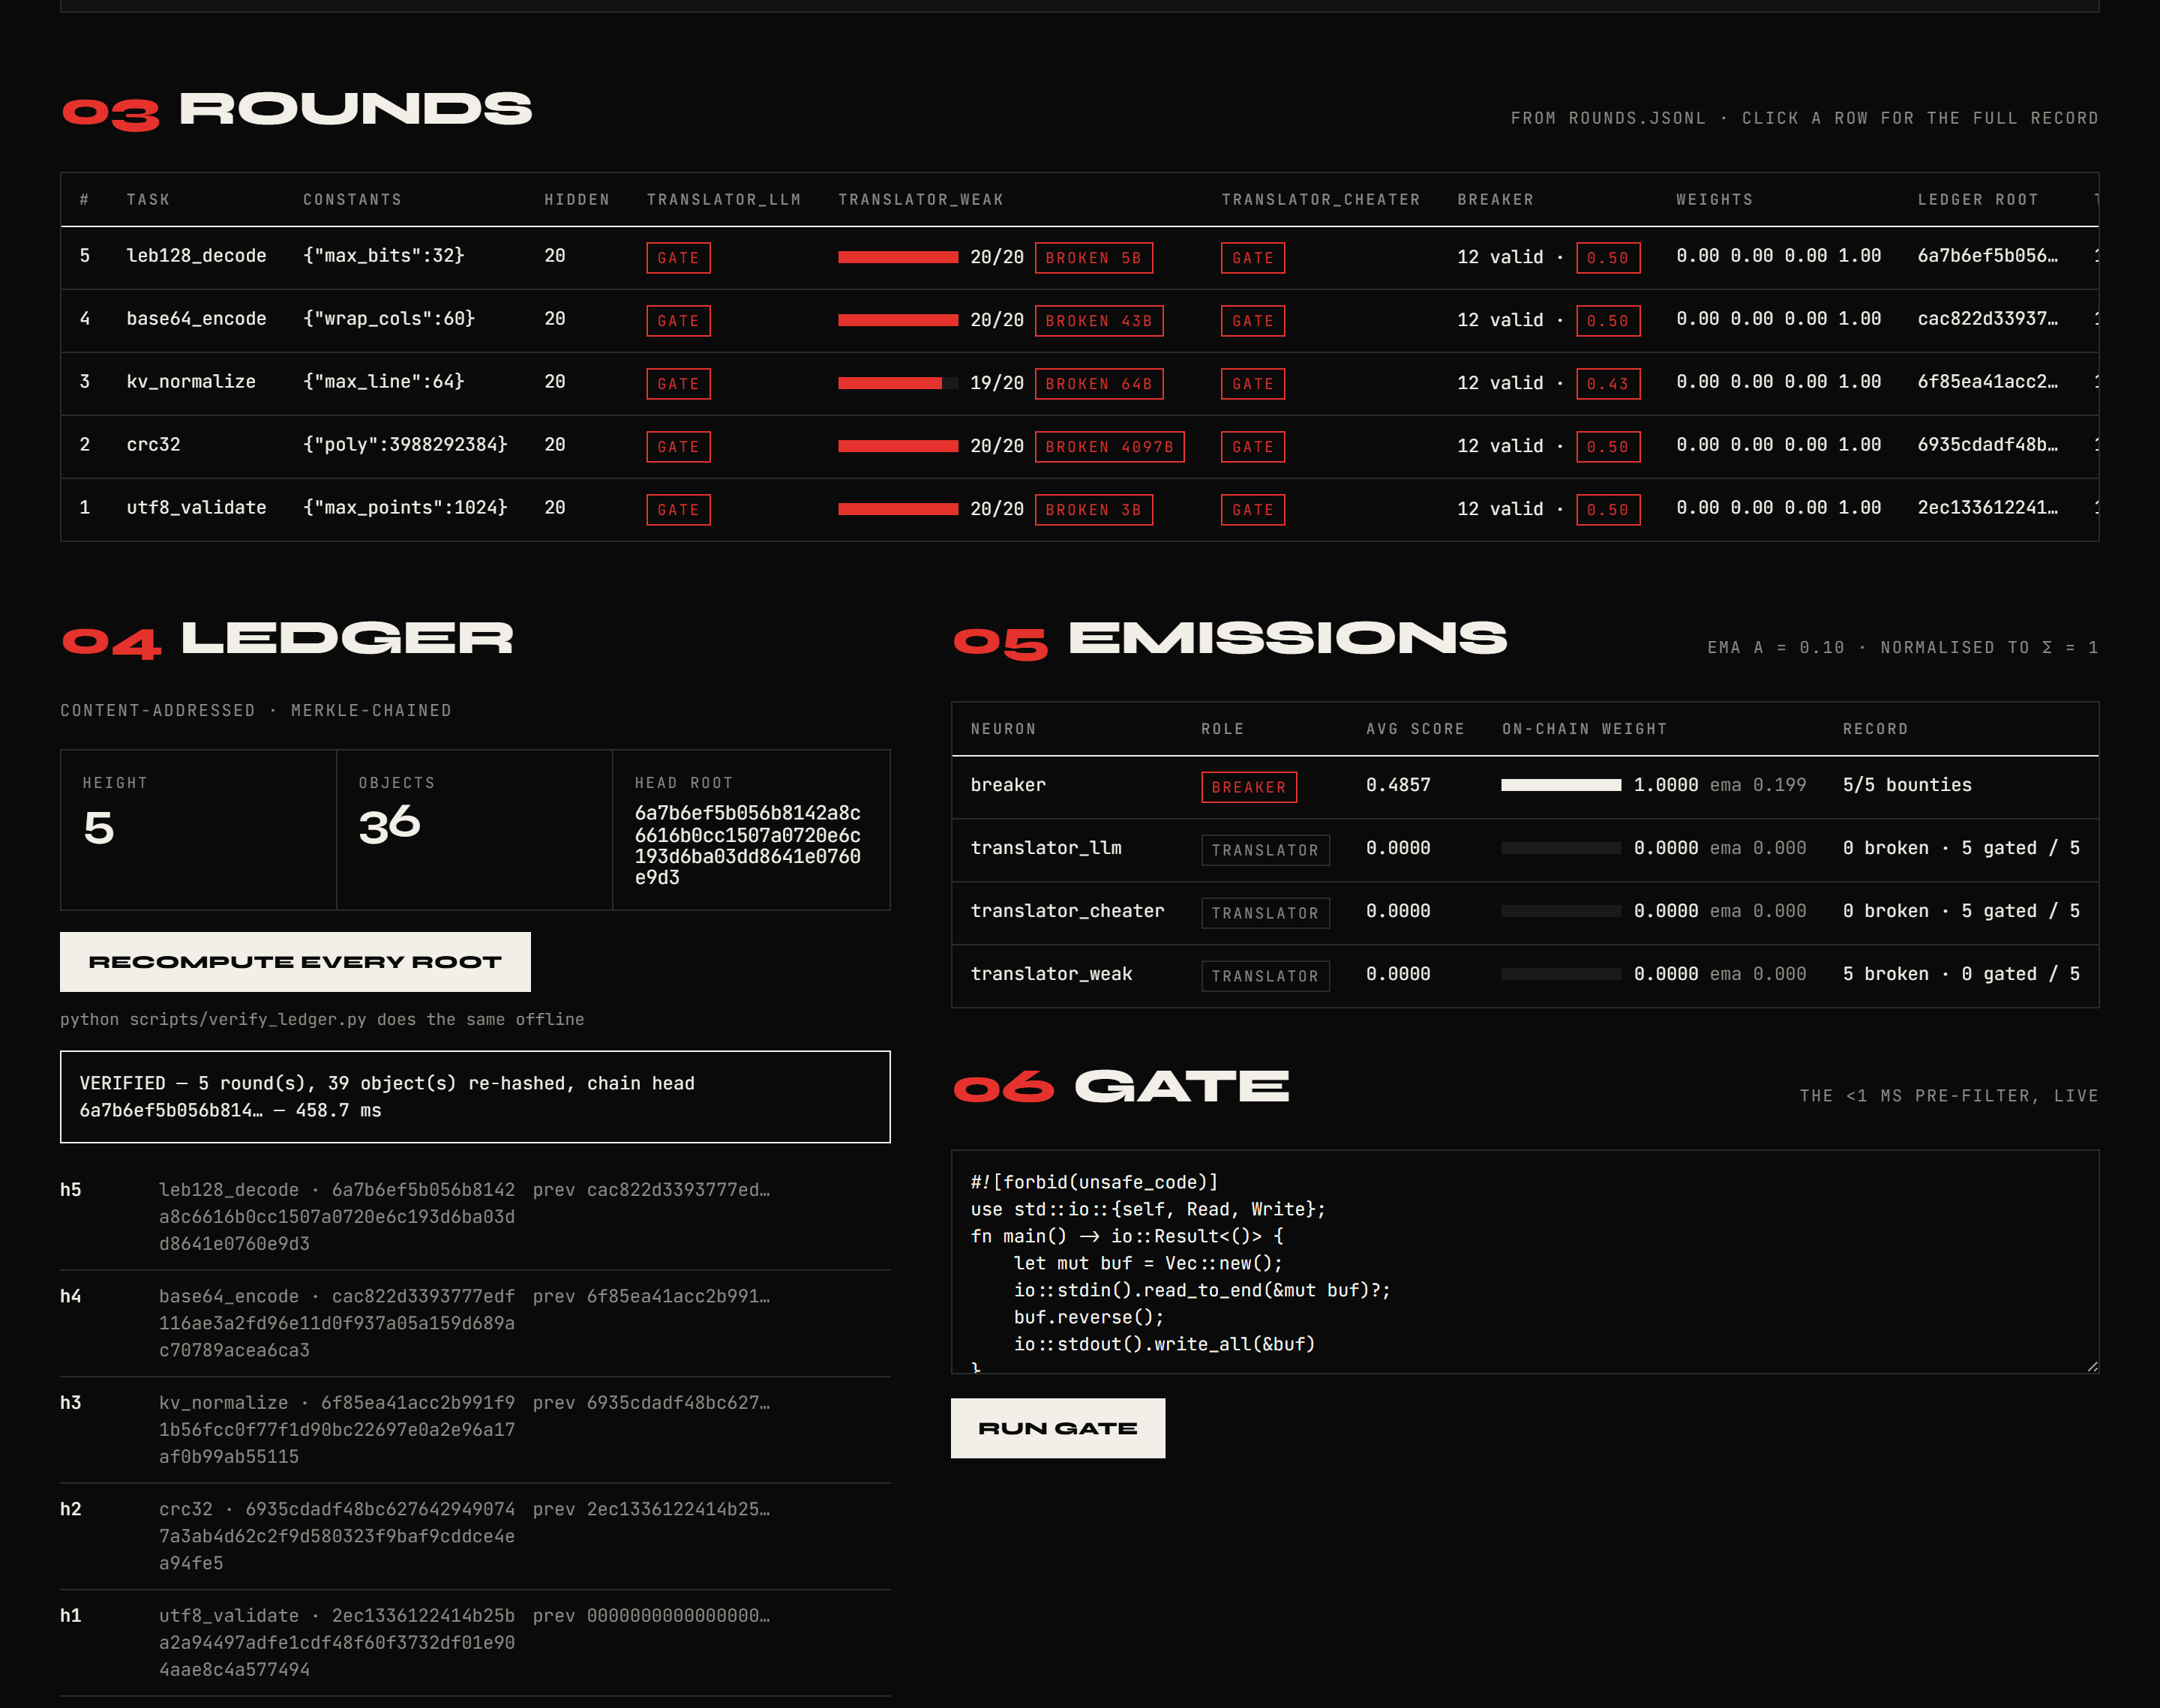
Every round is committed to a content-addressed, merkle-chained ledger: the C source, every Rust submission, every reproducer, every verdict. verify_ledger.py re-hashes the whole history offline and fails on any edit.
What exists today. Eight UB-free C programs with per-round constants (base64, INI normaliser, LEB128, UTF-8 validator, CRC-32, FNV-1a, RLE, chunk reversal), each with a planted-bug fixture that passes the hidden tests and falls only to the breaker. 38 tests. A live dashboard streaming each round over SSE with a proof-of-break panel. In real runs the breaker found a 3-byte surrogate, a 4097-byte buffer overrun, and a 5-byte LEB128 overflow — each on a translation that had passed 20/20 hidden tests.
The asset. Probus doesn't just translate code. It continuously mints verified (C, Safe Rust, verdict, adversarial input) tuples under a cryptographic root — the training and evaluation data the next generation of code models needs, produced by an economy rather than a lab.
Progress During Hackathon
All of it was built during the hackathon window:
Validator pipeline: static gate,
rustc -F unsafe_code, sandboxed differential execution, ASan/UBSan input validity, cubed scoring, 50% anti-collusion bounty, EMA weights,set_weightsLLM translator miner with a self-fuzzing repair loop (provider-agnostic; record/replay of model output with provenance)
Breaker miner: static boundary analysis + mutation fuzzer + ddmin minimisation; base64-safe synapse protocol
Task pool of 8 real-world-shaped C programs with per-round constants and CI-proven fixtures
Merkle-chained ledger with offline verifier
Live dashboard (FastAPI + SSE), unified miner CLI, demo and recording scripts
38 automated tests; MIT licensed
Fixed two validator bugs found along the way: non-zero exit codes were being treated as UB (discarding the inputs that test error paths), and a launch failure on both binaries was scored as a pass
Fundraising Status
Bootstrapped, no funding raised; not currently raising.